Device Pairing Sequences That Refine Authorization Flows in Multi-Region Recurring Merchant Setups
David Weber · Aug 8, 2026
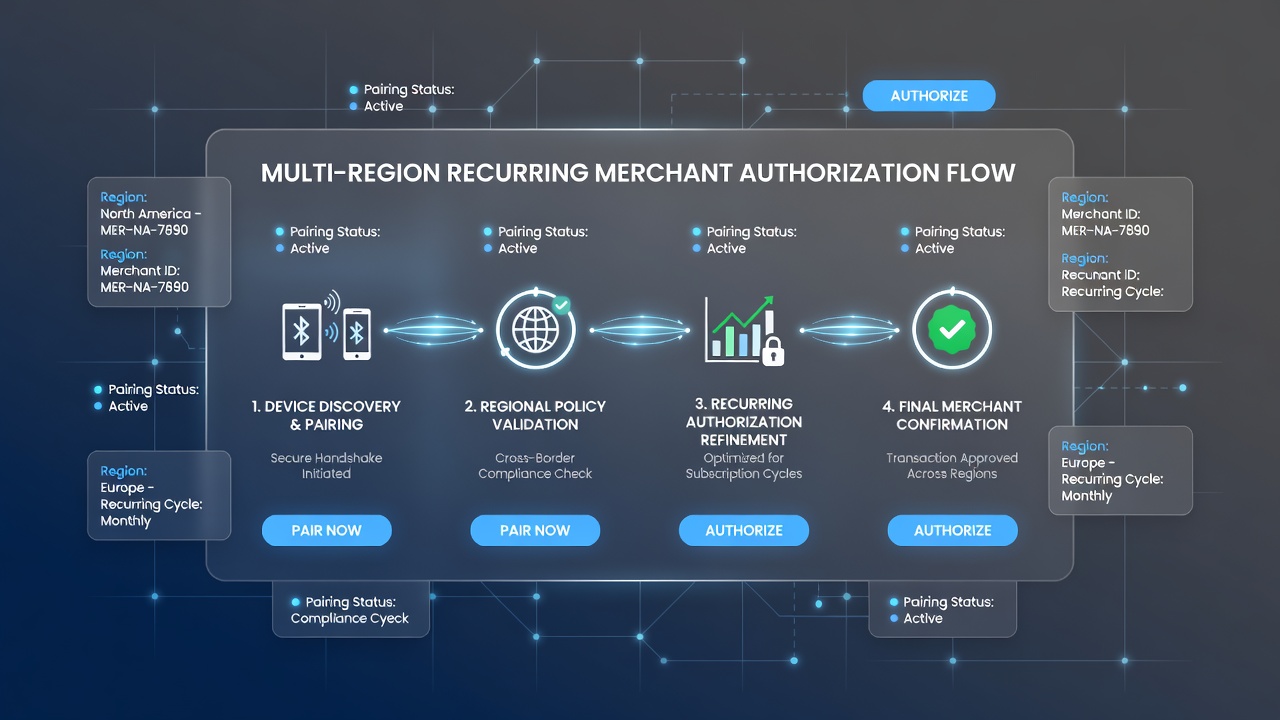
Device Pairing Sequences That Refine Authorization Flows in Multi-Region Recurring Merchant Setups
Device pairing sequences establish secure connections between merchant terminals and backend authorization systems in setups that span multiple regions and support recurring transactions, and these sequences incorporate cryptographic handshakes along with region-specific validation steps that align with local regulatory requirements. Research from payment networks indicates that structured pairing reduces failed authorization attempts by routing device credentials through tokenization layers before transaction data reaches acquirers, while the process begins with device discovery protocols that confirm hardware identities through unique identifiers stored in secure elements.
Those who manage multi-region recurring merchant operations note that pairing often follows a phased sequence where initial Bluetooth or NFC discovery leads into certificate exchange and mutual authentication, after which session keys are generated to encrypt subsequent recurring billing cycles. Data from industry reports shows that in August 2026 several payment processors updated their pairing firmware to incorporate post-quantum cryptography elements that address emerging threats across European and Asian markets simultaneously.
Core Components of Pairing Sequences
Pairing sequences typically integrate hardware attestation, network latency checks, and dynamic token issuance, and these elements work together because recurring merchant setups require consistent authorization across borders where currency conversion and tax rules differ. Observers report that the sequence starts with a challenge-response mechanism that verifies the terminal's firmware integrity before any customer data enters the flow, which prevents unauthorized devices from initiating subscription charges in regions governed by varying data protection standards.
Experts have observed that once attestation succeeds the system moves to key derivation using algorithms compliant with standards from bodies such as the Bank for International Settlements, and this step generates ephemeral keys that expire after each billing cycle to limit exposure in high-volume subscription environments. The process continues with region-aware routing that selects authorization endpoints based on merchant location and customer residency, ensuring compliance with local mandates without interrupting the recurring payment schedule.
Handling Multi-Region Authorization Refinements
Authorization flows gain precision when pairing sequences embed geolocation metadata and regulatory flags during the initial handshake, because merchants operating in multiple jurisdictions must satisfy distinct rules for recurring charges. Studies indicate that refined sequences incorporate fallback pathways that activate when primary authorization endpoints experience delays, and these pathways maintain transaction integrity by switching to secondary validators that have pre-established trust relationships with the paired device.
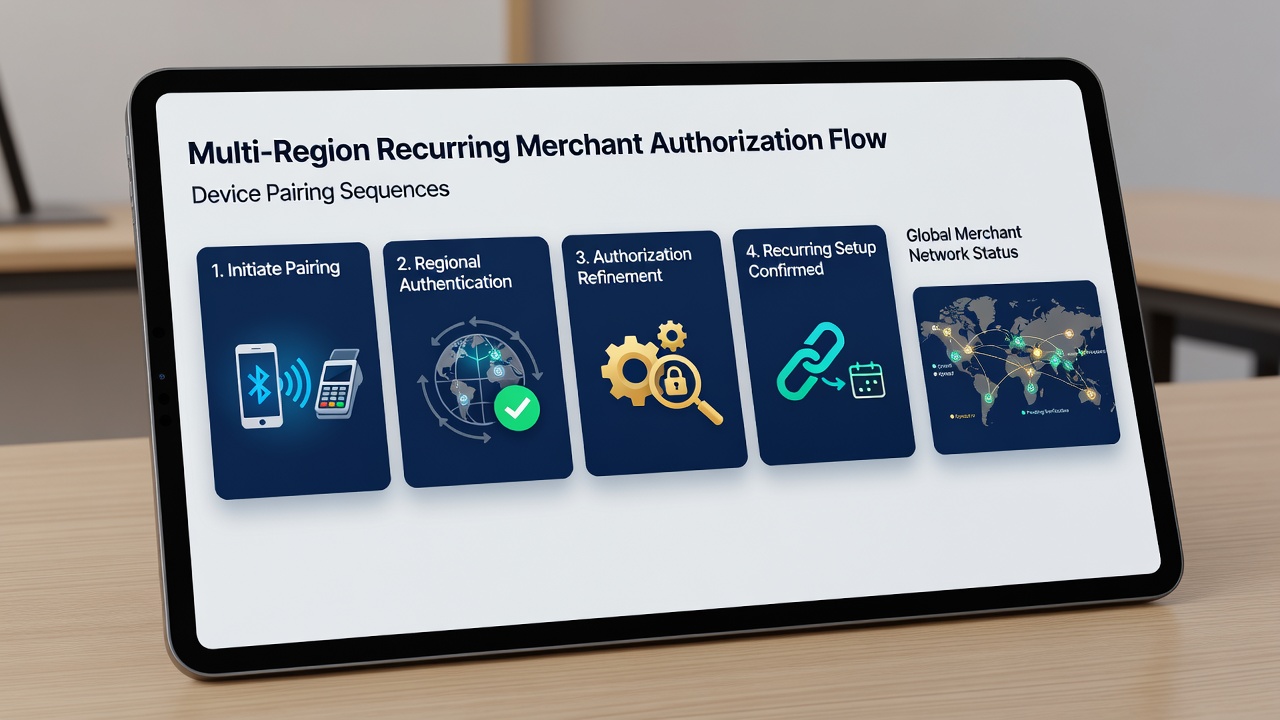
Those who've examined recurring merchant platforms find that pairing logs capture every step of the sequence for audit purposes, and these logs feed into analytics systems that detect patterns suggestive of device compromise across different time zones. In practice the sequence concludes with a confirmation packet that includes a hash of the session parameters, which both the terminal and the authorization server store for reconciliation during later billing events.
Technical Implementation Details
Implementation relies on standardized protocols such as those outlined in technical specifications from the PCI Security Standards Council, yet sequences are customized per region to accommodate local network conditions and device certification requirements. The pairing begins with a broadcast of supported cipher suites, after which the terminal and server negotiate the strongest mutually acceptable option before proceeding to certificate validation that checks revocation status through online certificate status protocol queries.
Further along the sequence, recurring authorization tokens are issued with embedded constraints that limit their use to specific merchant categories and geographic zones, and this constraint mechanism reduces the risk of token misuse when subscriptions span continents. Figures from transaction monitoring platforms reveal that merchants adopting these refined sequences experience measurable improvements in authorization success rates during peak recurring billing periods.
Conclusion
Device pairing sequences continue to evolve as recurring merchant operations expand across regions, and the refinements they introduce to authorization flows rest on layered cryptographic and procedural safeguards that maintain consistency without sacrificing adaptability. Those managing these systems rely on documented sequences to meet both operational and compliance demands that shift with each new market entry.